AI agents with memory: deciding what they can share
TokenShift Executive Note
AI-translated from the original French version.
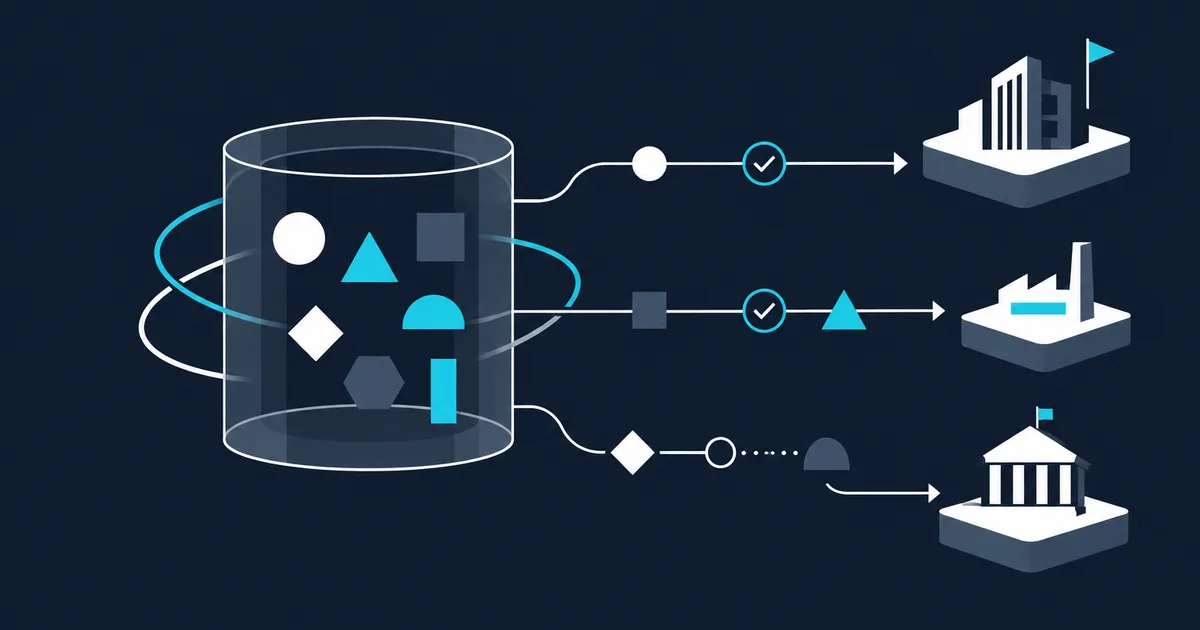
An agent may need to consult a note to handle a case without being authorised to share it. With persistent memory, that note may remain accessible when the agent moves to another task or speaks to someone else. This makes it necessary to decide what the agent retains, for what purpose and with whom it may share it.
Meta presents Active Memory, associated with Muse Wonder, as a way to retrieve relevant information from one conversation to the next. The company also says it has trained its models to avoid sharing private information without authorisation. These stated capabilities do not, however, define the sharing rights that apply within a bank or insurer. Meta, 2026
Prepare information for the third party
Consider a hypothetical scenario. An insurer asks an agent to arrange a visit after a claim. The case file contains the property's address, the policyholder's availability and an internal note about a contractual dispute. The service provider asks for details before travelling to the property. The address and availability may be necessary. That request does not justify sharing the note.
We recommend building this distinction into access controls. The component that arranges the visit consults the necessary parts of the case file. The component that communicates with the service provider receives a brief limited to information that may be shared for this assignment. It then has less confidential information to filter out itself.
This separation takes work: defining and maintaining the brief, and deciding how to handle requests it cannot answer. The business team decides what the service provider needs to receive. The technical team translates that decision into access rights and controls, involving the DPO and CISO according to the data and mechanisms concerned. The process owner remains clearly identified.
OWASP recommends limiting agents' functions and permissions, and having the systems they call enforce authorisations. OWASP, 2025 In our scenario, this means:
- The sending connector can access the brief for the designated service provider, without access to the whole case file.
- A request about the contractual dispute is referred to an authorised person.
- If sending requires human approval, the person sees the recipient and the exact content proposed.
The same principle applies over time. Authorisation for one specific message does not cover every subsequent exchange. At the end of the assignment, the process owner checks what should remain accessible and for how long. A change of service provider or the reopening of the case calls for a fresh review of sharing rights.
Test the conversation through to the end
The first response is not enough to assess these controls. In the Loose Lips preprint, the authors observe more disclosures as exchanges continue in certain configurations. Their study uses synthetic profiles, dialogues in English and automated evaluators. The comparison by conversation length covers only a subset of the models studied. It measures neither incidents in businesses nor Muse Wonder's behaviour. Sharma and co-authors, 2026
We draw a practical conclusion: tests should include follow-up requests and conversations resumed after an interruption. Fictional case files can combine information needed for the assignment with information that must not be shared. The team varies the recipient and their requests, then examines the entire exchange: what data was sent, where did it come from and what authorisation allowed it to be sent?
These tests should also show how work proceeds when a request goes beyond the brief. A justified block and an unnecessary one call for different corrections. It may be necessary to add to the brief, revise a rule or retain human approval.
Time savings should be measured across this complete process, with service quality comparable to the existing process. Preparing data, approving messages, resuming exchanges and correcting errors all take staff time. That time should be considered alongside resolution time, disclosures outside the permitted scope and blocked requests.
Before allowing agents to send messages autonomously to third parties, the process owner should be able to review a complete conversation, the information actually shared and the handling of an out-of-scope request. Satisfactory tests make it possible to consider a limited use, without guaranteeing that no future disclosure will occur. This review should be repeated when the model, memory or connectors change.
Sources
- Meta, 2026: introduction to Muse Wonder and Active Memory.
- Sharma and co-authors, 2026: Loose Lips, methods, results and limitations.
- OWASP, 2025: excessive agency, permissions and controls on actions.